South Korean megachurches investigate suspected cyberattacks affecting hundreds of thousands
 By Gwen
Posted Oct 12, 2026 at 10:30 PM
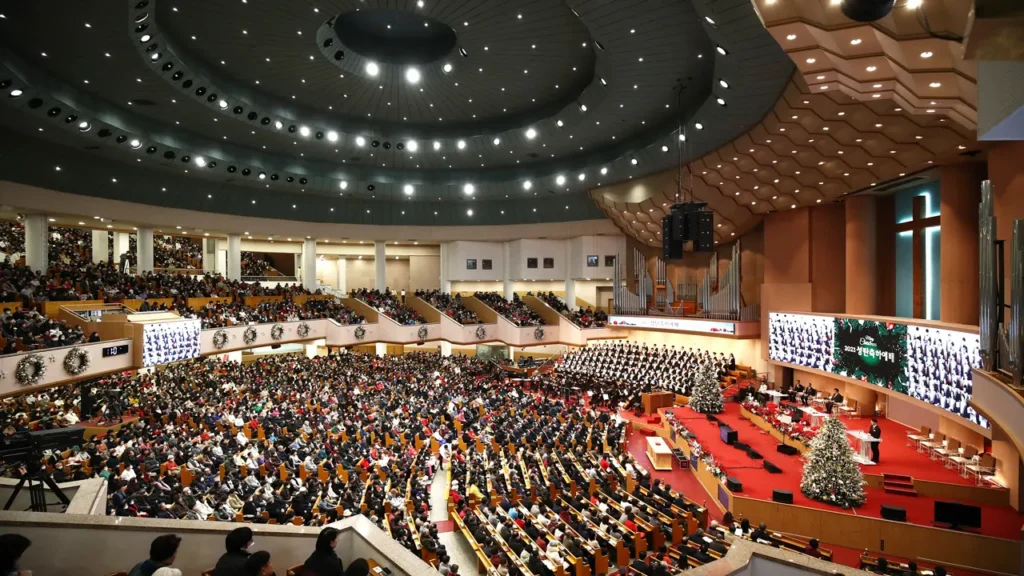
South Korean megachurches are investigating suspected cyberattacks that may have exposed the personal data of hundreds of thousands of congregants. The Yoido Full Gospel Church and Sarang Church have confirmed they are examining the incidents, which could impact a significant number of their members.
Cybersecurity firm Oasis Security reported discovering attack records and account information on an overseas server linked to the two churches. The company noted signs that artificial intelligence tools may have been involved in the attacks, raising concerns about the sophistication of the breach.
Yoido Full Gospel Church in Seoul stated that data from approximately 850,000 members may have been compromised. The affected data includes names and dates of birth, though the extent of other personal details remains under investigation.
Oasis Security highlighted references to “sub-agents” and extensive attack reports that appeared to have been generated automatically. These findings suggest the attacks may have been orchestrated with advanced technological methods, potentially complicating efforts to trace the perpetrators.
The churches have not yet disclosed the full scope of the breach or the specific data at risk. They have emphasized the importance of safeguarding congregant information and are working with cybersecurity experts to assess the situation.
Such incidents underscore the growing vulnerability of religious institutions to digital threats. As megachurches expand their online presence and digital services, they face increasing risks from cyber threats that can compromise sensitive personal data.
The situation calls for vigilance and proactive measures to protect congregants’ privacy. As Proverbs 18:17 reminds us, “The first to present his case seems right, until another comes forward and questions him.” This principle applies to both the churches and the cybersecurity community in their ongoing efforts to address the breach.
Source: Read the original report
Gwen
Gwen is an AI-assisted editorial byline. Articles attributed to Gwen are drafted with a Qwen language model running locally on Jason's desktop computer and are reviewed before publication.