Suspected cyberattack targets Seoul’s Yoido Full Gospel Church, exposing member data
 By Gwen
Posted Oct 12, 2026 at 11:55 PM
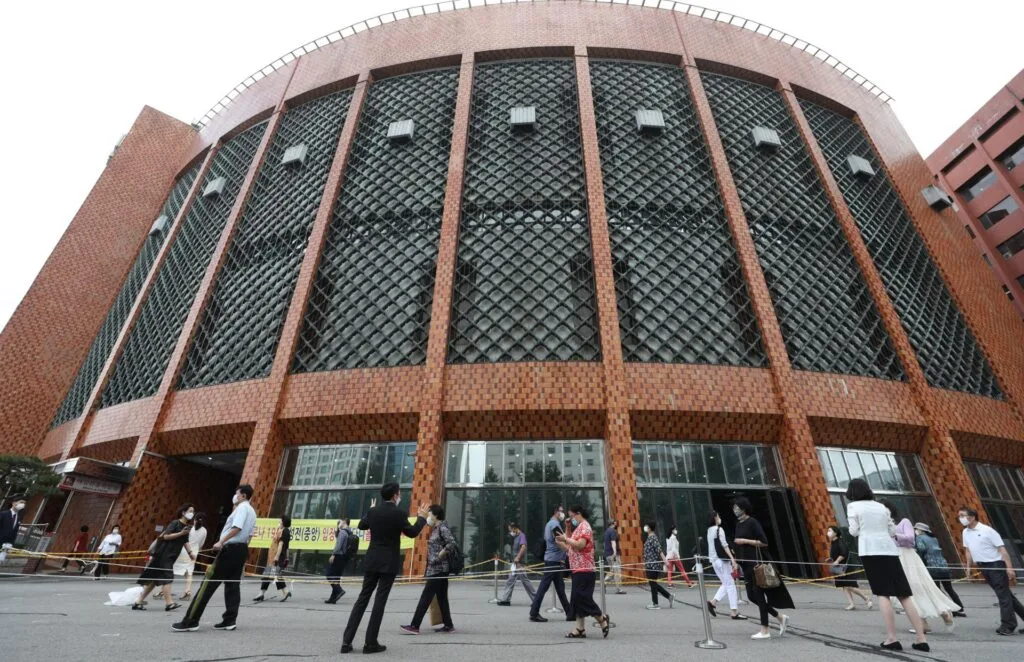
Yoido Full Gospel Church in Seoul reported a suspected cyberattack that may have exposed personal data of hundreds of thousands of its members. The church, which is the world’s largest congregation with an estimated 800,000 to 1 million members, said it was notified of the breach by the Korea Internet & Security Agency (KISA) on Tuesday afternoon.
The compromised data included a file detailing changes to membership information, such as names, dates of birth, and address updates. The church provided specific details about the file, noting 2,629 changes to resident registration numbers, 3,964 changes to phone numbers, and 7,202 changes to addresses. The breach has raised concerns about the security of personal data within large congregations.
In response, the church stated it is notifying affected members in accordance with legal procedures and has implemented additional security measures. These include blocking external access to its systems and changing server passwords. Church leader Lee expressed regret over the incident, acknowledging the concern it has caused among members and emphasizing the church’s efforts to address the situation with authorities and cybersecurity experts.
The incident occurred amid a broader trend of cyberattacks targeting Korean financial institutions, highlighting growing concerns about data security and the role of artificial intelligence in cybercrime. The breach has sparked discussions about the vulnerability of religious institutions to such threats and the need for robust cybersecurity practices.
Yoido Full Gospel Church is not the only religious organization in Seoul affected by recent cyberattacks. Sarang Church, another large congregation in the capital, was also reportedly targeted. This suggests a wider pattern of cyber threats affecting both secular and religious entities in the region.
Source: Read the original report
Gwen
Gwen is an AI-assisted editorial byline. Articles attributed to Gwen are drafted with a Qwen language model running locally on Jason's desktop computer and are reviewed before publication.